The Judgment Gap in Market Abuse Compliance
Three Areas of EU MAR Exposure
📅 August 25, 2026

Banks know the black-letter rules of the EU’s Market Abuse Regulation reasonably well. Article 17 on public disclosure, Article 14 on the prohibition of insider dealing, Article 11 on market soundings: these are documented, trained on, and built into policy manuals across the industry. The exposure that keeps surfacing in supervisory reviews and enforcement notices sits in the judgment calls layered on top of those rules.
Three areas account for a disproportionate share of that exposure: delayed disclosure decisions, information barriers, and market soundings. Each one depends less on knowing the rule and more on a person or a process reassessing a live situation correctly, under time pressure, without the benefit of hindsight.
Article 17(4) of the Market Abuse Regulation lets an issuer delay public disclosure of inside information where three conditions hold:
The test appears simple but applying it consistently, over the life of a delay that might run for weeks, is where banks struggle.
The AMF’s own guidance on inside information disclosure makes a point worth noting: the ability to rely on the delayed disclosure exception ceases the moment any one of the three conditions is no longer fulfilled, not at some later point when someone gets around to checking. Regulators expect firms to keep testing it as circumstances change, and ESMA’s guidelines on delayed disclosure reinforce that the assessment of legitimate interest and confidentiality has to hold for as long as the delay continues, not only at the point the decision was first made.
In practical terms, this means three things commonly go wrong:
This last point is critical. Article 17(4) requires a bank to notify its national competent authority of the delay once the information is disclosed, and that authority can request a written explanation of how the conditions were satisfied throughout. The strength of a bank’s position rests almost entirely on what it can show, not on what it can now argue. A delay that was reasonable on day one but never revisited on paper is difficult to defend on day thirty, regardless of how sound the original reasoning was.
The governance fix involves naming an owner for the delayed decision, setting a cadence for reassessment tied to specific triggers rather than a calendar default, and keeping records current throughout the delay rather than reconstructing it after the fact. While this may appear straightforward, it tends to be harder to embed.
Every bank of any size has an information barriers policy — physical separation between public and private side, systems access controls, formal wall-crossing procedures, and a restricted list that gets updated as new material non-public information enters the building. On paper, the architecture is sound, but the gap shows up in how people behave once a deal is moving fast.
ESMA’s own review of the MAR framework makes the underlying point directly: insider lists remain a key tool in market abuse investigations, precisely because they let an investigator check who had access to what, when, and whether a wall-crossing or disclosure was properly controlled. A wall-crossing procedure is only as strong as the insider list and the access log sitting behind it.
National regulators have not hesitated to enforce on this point directly. In one recent decision, France’s AMF Enforcement Committee fined three legal entities and eight individuals for insider dealing breaches that included a failure to maintain and update insider lists properly, with penalties ranging up to €1,000,000 against individuals.
The gatekeeper model works well as a design principle. It breaks down at the point where deal teams route around it because a policy did not anticipate exactly how the leak happened. Four patterns recur across how these failures happen inside a bank:
The point examiners repeatedly come back to is that barriers are tested by tracing how information truly moved, not by reading the policy document that describes how it is supposed to move. That distinction is the whole point, a wall can be correctly designed and still fail, because the test that matters is whether it holds up when people are busy, moving quickly, and communicating through channels the policy writer never pictured.
Article 11 of the Market Abuse Regulation offers a safe harbor for disclosing market participants who follow a defined process when gauging investor interest ahead of a transaction— standardized scripts, confirmation of the recipient’s insider status, cleansing communications once the information is no longer needed, and records retained for five years. Get the mechanics right, and a disclosure that would otherwise look like unlawful tipping is protected. Get them wrong, and the safe harbor simply isn’t available when needed most.
The gatekeeper model sits at the center of ESMA’s guidelines for exactly this reason; a single, designated point of contact is meant to control who gets wall-crossed for a sounding, confirm their insider status, and log the disclosure properly. The mechanism is worth describing in full because it is where the safe harbor most often fails. Gatekeepers act as the first point of contact for a disclosing market participant requesting consent to conduct a sounding, and this arrangement is designed to keep the process consistent and limit the chance of a leak. The risk sits just after that point because once the gatekeeper has given consent, information can end up shared with additional individuals at the recipient firm over email or chat, with the circle of recipients expanding without any real control over who is being added or whether each of them has actually been wall-crossed by the gatekeeper.
This pattern captures why market soundings are a genuine grey area rather than a simple compliance checklist. The formal safe harbor framework can be followed to the letter at the point of initial contact, and the protection can still be lost three exchanges later, when a well-meaning banker copies a colleague into a thread without checking whether that colleague has been through the same process. Three related issues compound this:
The stakes are direct. Lose the safe harbor and a disclosure that was defensible under Article 11 becomes a live instance of unlawful disclosure or, depending on what followed, insider dealing. The mechanics are not a formality around the substance. They are the substance.
Delayed disclosure, information barriers, and market soundings look like three separate compliance domains with three separate rules. What they share is more instructive than what separates them. Each one depends on someone actively reassessing a live, moving situation.
Banks tend to invest more in the initial policy design but underinvest in the ongoing judgment layered on top of it. Training that covers only the rule and does not include grey areas creates teams that can recite Article 17(4) without being able to recognize, six weeks into a live delay, whether it still holds. Documentation practices that record the decision but not the reasoning behind it leave a bank exposed the moment a regulator asks not what was decided, but why, and whether that reasoning was ever revisited. And controls built around an assumption of good faith, rather than a genuine test for whether the assumption still holds, will look robust right up until the point they are tested.
There is a talent side to this too. The people making these calls, MLRO-adjacent compliance staff, deal-team gatekeepers, disclosure committee members, need working fluency in the grey zones themselves, not just familiarity with the underlying articles. That fluency is built through training and exposure to real supervisory findings and real judgment calls.
Grey zones like these rarely show up the same way twice.
A delayed decision that trips up one bank’s disclosure committee looks nothing like the wall-crossing gap that catches another’s deal desk. Generic course libraries can’t account for that variation, and they usually don’t try to.
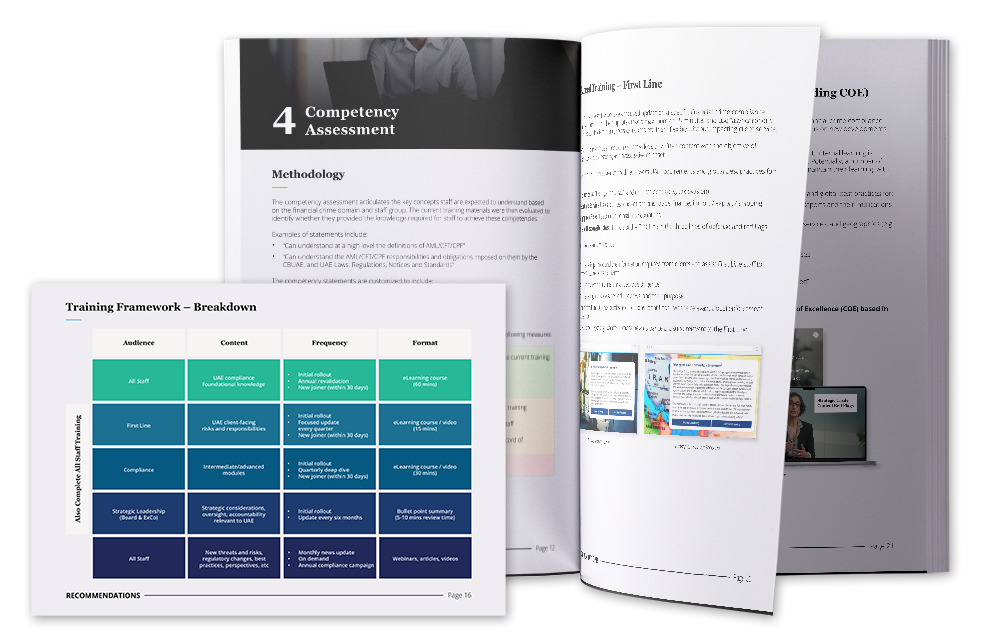
At IFI, our training needs assessment starts by mapping where your specific exposure sits; which judgment calls your compliance officers, gatekeepers, and deal teams are making under pressure, and where the current training leaves a gap between knowing the rule and knowing how to apply it. From there, our custom program development builds learning around those exact pressure points, drawing on a team of former regulators and compliance officers who’ve made these calls themselves, rather than adapting a standard curriculum to fit.
 https://finintegrity.org/wp-content/uploads/2026/09/august-2026-se-report-bg.jpg
888
1184
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-09-02 07:00:562026-09-01 13:19:24August Monthly Sanctions and Export Controls Report
 https://finintegrity.org/wp-content/uploads/2026/08/beyond-the-course-library-bg.jpg
1060
1800
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-08-12 07:00:232026-08-11 12:42:07Beyond the Course Library
 https://finintegrity.org/wp-content/uploads/2026/08/july2026-se-bg.jpg
1177
1800
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-08-04 07:00:452026-08-04 09:42:02July Monthly Sanctions and Export Controls Report
 https://finintegrity.org/wp-content/uploads/2026/07/guide-to-market-abuse-bg.jpg
1067
1600
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-07-29 07:00:472026-07-28 12:45:11A Financial Institution’s Guide to Updated EU Market Abuse Regulation
 https://finintegrity.org/wp-content/uploads/2026/07/hiddenfactor-compliance-bg.jpg
1200
1800
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-07-22 07:00:132026-07-21 11:49:18The Hidden Factor Behind Effective Compliance Training
 https://finintegrity.org/wp-content/uploads/2026/06/june2026-se-report-bg.jpg
798
1200
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-07-01 07:00:392026-07-02 10:28:58June 2026 Sanctions and Export Controls Report
 https://finintegrity.org/wp-content/uploads/2026/06/who-owns-bg.png
667
1000
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-06-10 07:00:162026-06-10 11:47:15Who Owns the Risk?
 https://finintegrity.org/wp-content/uploads/2026/06/may-bg-2026-se.jpg
1200
1800
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-06-03 07:00:142026-06-02 14:36:12May 2026 Sanctions and Export Controls Update
 https://finintegrity.org/wp-content/uploads/2026/03/understandingfatf-bg.jpg
1000
1500
IFI
https://live-black-pebble.pantheonsite.io/wp-content/uploads/2023/12/GIFI-Placeholder2.png
IFI2026-05-13 07:00:082026-05-22 13:26:47Understanding the FATF: A Guide for Private Sector Stakeholders Part 3

 National Bank of Yemen Launches Enterprise-Wide Compliance Training with IF...